In the current, complex and dynamic context of cyber security, collaboration with partners is of strategic importance for Safetech Innovations. This section presents our partnerships for integrated solutions and provides information to our resellers of our own and distribution channel products.
In its systems integrator role, Safetech has contractual partnership relationships with a diverse set of companies with a determining role in the field of cyber security. The Technology Partners section contains brief descriptions of them.
Resellers
Documents and information for reseller companies of Safetech Innovations’ own products and products and services for which it acts as a distributor
Technology news
Articles written by Safetech Innovations describing how the solutions in the company’s portfolio work, the problems addressed, the benefits obtained, as well as aspects that require attention in order to achieve optimal results
Safetech Innovations S.A. has been providing cyber security services and solutions tailored to the needs of organizations since 2011. Many Romanian organizations have chosen Safetech's solutions and services for system integration, consulting, vulnerability management, operations outsourcing, security audit, in order to improve their level of cyber security.
On Feb. 6 2023 Safetech Innovations shares started trading on the Main Market of the Bucharest Stock Exchange under the symbol SAFE. This section contains information and documents intended for SAFE investors. For information on the evolution of share prices, we invite you to follow our profile on the BVB website.
Since 2011, we have maintained our strategic focus on cyber security, we act as a Managed Security Service Provider, and to date we have completed more than 600 testing and consulting projects and participated in more than 100 critical infrastructure security projects in the United States United, EU, China, India, Canada, Brazil, Morocco, Singapore, Philippines and New Zealand.
In the current, complex and dynamic context of cyber security, collaboration with partners is of strategic importance for Safetech Innovations. This section presents our partnerships for integrated solutions and provides information to our resellers of our own and distribution channel products.
In its systems integrator role, Safetech has contractual partnership relationships with a diverse set of companies with a determining role in the field of cyber security. The Technology Partners section contains brief descriptions of them.
Resellers
Documents and information for reseller companies of Safetech Innovations’ own products and products and services for which it acts as a distributor
Technology news
Articles written by Safetech Innovations describing how the solutions in the company’s portfolio work, the problems addressed, the benefits obtained, as well as aspects that require attention in order to achieve optimal results
Safetech Innovations S.A. has been providing cyber security services and solutions tailored to the needs of organizations since 2011. Many Romanian organizations have chosen Safetech's solutions and services for system integration, consulting, vulnerability management, operations outsourcing, security audit, in order to improve their level of cyber security.
On Feb. 6 2023 Safetech Innovations shares started trading on the Main Market of the Bucharest Stock Exchange under the symbol SAFE. This section contains information and documents intended for SAFE investors. For information on the evolution of share prices, we invite you to follow our profile on the BVB website.
Since 2011, we have maintained our strategic focus on cyber security, we act as a Managed Security Service Provider, and to date we have completed more than 600 testing and consulting projects and participated in more than 100 critical infrastructure security projects in the United States United, EU, China, India, Canada, Brazil, Morocco, Singapore, Philippines and New Zealand.
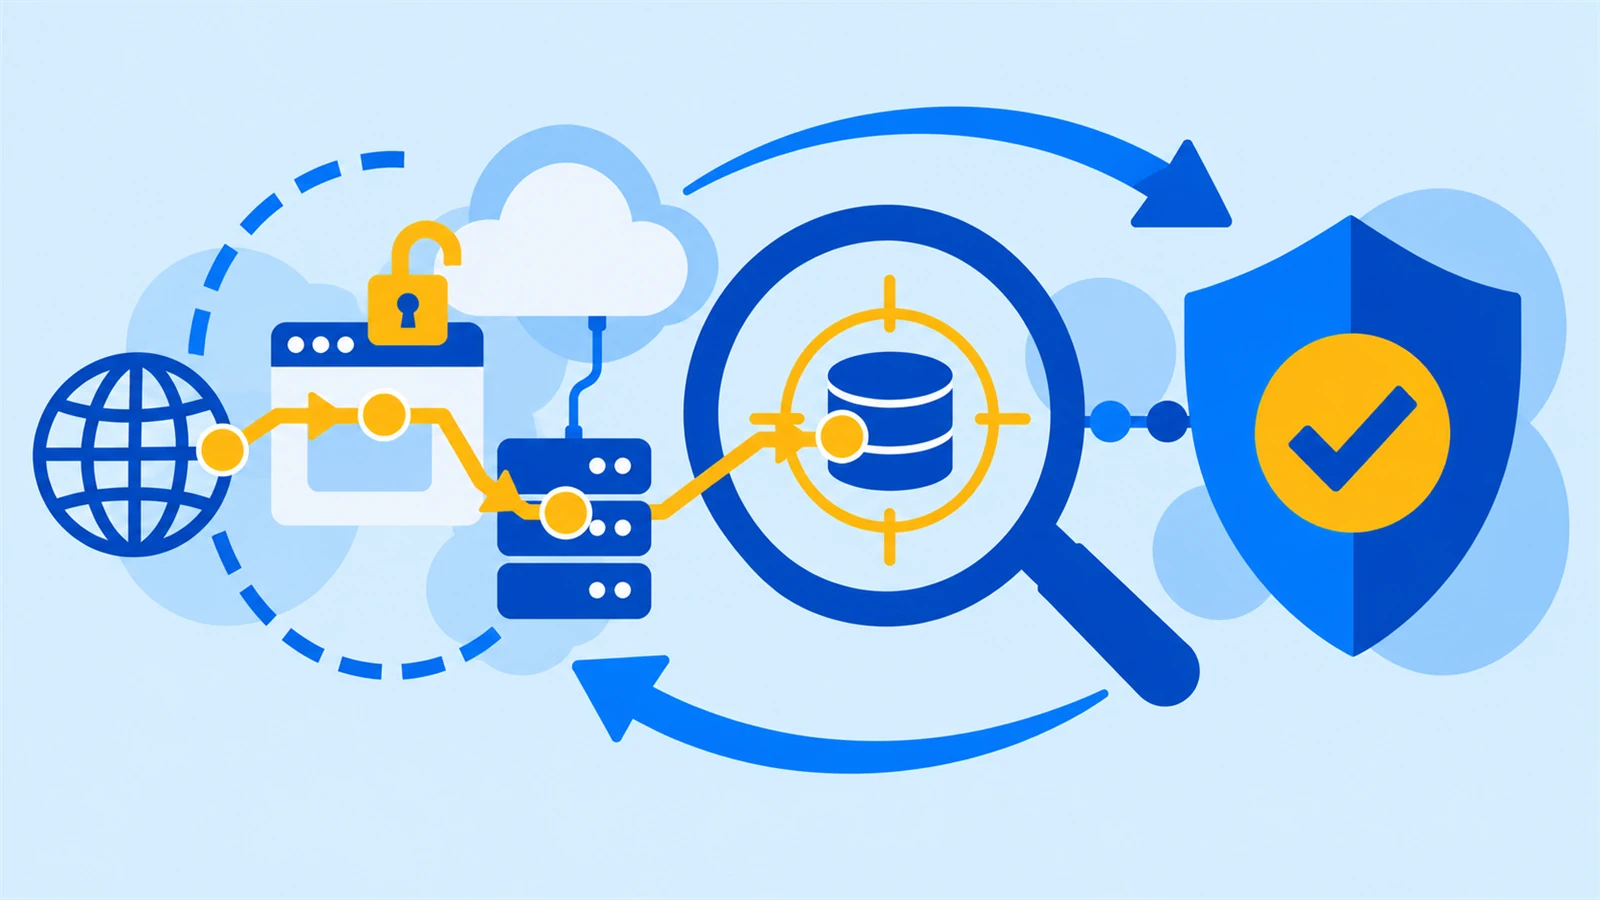
Vulnerabilities change with infrastructure, applications, and threats. Safetech Innovations' Recurrent Vulnerability Management service helps you identify security issues, prioritize remediation, and track evolving risk through a monthly schedule.
We correlate the results of the scans with the specialists' analysis and with information about the evaluated environment. The organization receives recommendations for the technical teams and an image of the priorities for management, within the agreed perimeter.
Utility and benefits
The service is aimed at organizations that need repeated vulnerability assessments and follow-up of remediation measures, including in mixed or frequently changing infrastructures. By collaborating with Safetech you benefit from:
Visibility into vulnerabilities
Identify issues in internal and external assets included in the service
Context-based priorities
Ordering findings by severity, exploitability, and impact on the organization
Remediation support
Recommendations and a plan that can be used by the responsible teams
Tracking progress
Highlighting new vulnerabilities, fixed vulnerabilities and the evolution of risk over time
Management reporting
Technical and executive results that support decisions on the measures and resources needed
Service Methodology and Characteristics
The Recurring Vulnerability Management service has the following characteristics:
Domain definition and authorization
We determine covered assets, internal and external scans, access conditions, and execution windows. We agree on scan frequency, severity thresholds, prioritization criteria, and remediation responsibilities, along with contacts and exclusions.
Scanning and analysis of findings
We run scans within the authorized perimeter and analyze the results to identify and classify relevant vulnerabilities. Checks track agreed assets and services, within the limits of access and available information. Analysis of findings supports filtering out irrelevant results and clarifying those that require further investigation.
Nessus Professional, Nessus Expert and the internal Safetech Vulnerability Management tool can be used, according to the scope and requirements of the collaboration. The selection of technologies and the conditions of use of licenses are defined for the contracted service.
Contextual prioritization
The assessment takes into account the technical severity, including CVSS, along with the context of the organisation. We analyse factors such as the existence and feasibility of using exploitation methods and the potential impact on the systems assessed, in order to establish the order of interventions.
Safetech’s own scoring methodology supports risk assessment at the level of the assets and infrastructure included. The results help teams focus their efforts on priority vulnerabilities and allow the evolution of risk to be compared between the periods analyzed.
Remediation planning
We formulate recommendations and a prioritized remediation plan. We clarify the findings and proposed measures with the organization’s leaders, to support the planning of actions.
The implementation of fixes is the responsibility of the designated teams according to the agreed responsibilities. Patch management and configuration modification are activities that are defined distinctly from the analysis and recommendations of the Vulnerability Management service.
Rescanning and tracking progress
We track the retest and verify remediation through rescans in the domain and at the agreed intervals. We compare the results for the included assets and highlight new vulnerabilities, findings that remain open and measures verified. The evolution of risk scores and explanations of the changes observed support the prioritization for the next period.
Deliverables, mode of collaboration, and complementary services
Deliverables
The deliverables of the recurring program are:
Monthly scan report — findings and verification results for valued assets.
Top of prioritized vulnerabilities — issues that need attention, sorted according to agreed criteria.
Remediation plan — recommended measures for identified vulnerabilities.
Risk dashboard — visibility into the situation and evolution of the risk in the field of the service.
Executive report — findings and priorities presented to management.
The content of the reports, the severity thresholds and the acceptance criteria are established for each collaboration. The follow-up of the evolution takes into account the coverage of scans and changes in the infrastructure.
Collaboration mode and complementary services
Vulnerability Management is a monthly recurring service. The frequency of scans, rescans, and updating of information in the dashboard is agreed based on assets, access, and objectives. The scan schedule is defined separately from the coverage of SOC monitoring services.
Vulnerability and patch management auditing evaluates the organization’s processes and controls. Infrastructure penetration testing aims to identify and exploit vulnerabilities in an authorized manner. Rapid assessment of the external attack surface is also a distinct service that is contracted separately.
For operational threat monitoring and treatment, you can select SOC/MDR services, with their own objectives and responsibilities.
What recommends us?
The scoring methodology developed internally by Safetech correlates the technical severity of vulnerabilities with the possibility of exploitation and the impact on the organization. Contextual analysis helps teams set remediation priorities at the level of the assets and infrastructure included in the service.
Our experience in security testing and operations supports the interpretation of findings and the formulation of practical recommendations. We follow the evolution of vulnerabilities and risk scores, so that the organization understands the changes observed and can evaluate the progress of the measures implemented.