In the current, complex and dynamic context of cyber security, collaboration with partners is of strategic importance for Safetech Innovations. This section presents our partnerships for integrated solutions and provides information to our resellers of our own and distribution channel products.
In its systems integrator role, Safetech has contractual partnership relationships with a diverse set of companies with a determining role in the field of cyber security. The Technology Partners section contains brief descriptions of them.
Resellers
Documents and information for reseller companies of Safetech Innovations’ own products and products and services for which it acts as a distributor
Technology news
Articles written by Safetech Innovations describing how the solutions in the company’s portfolio work, the problems addressed, the benefits obtained, as well as aspects that require attention in order to achieve optimal results
Safetech Innovations S.A. has been providing cyber security services and solutions tailored to the needs of organizations since 2011. Many Romanian organizations have chosen Safetech's solutions and services for system integration, consulting, vulnerability management, operations outsourcing, security audit, in order to improve their level of cyber security.
On Feb. 6 2023 Safetech Innovations shares started trading on the Main Market of the Bucharest Stock Exchange under the symbol SAFE. This section contains information and documents intended for SAFE investors. For information on the evolution of share prices, we invite you to follow our profile on the BVB website.
Since 2011, we have maintained our strategic focus on cyber security, we act as a Managed Security Service Provider, and to date we have completed more than 600 testing and consulting projects and participated in more than 100 critical infrastructure security projects in the United States United, EU, China, India, Canada, Brazil, Morocco, Singapore, Philippines and New Zealand.
In the current, complex and dynamic context of cyber security, collaboration with partners is of strategic importance for Safetech Innovations. This section presents our partnerships for integrated solutions and provides information to our resellers of our own and distribution channel products.
In its systems integrator role, Safetech has contractual partnership relationships with a diverse set of companies with a determining role in the field of cyber security. The Technology Partners section contains brief descriptions of them.
Resellers
Documents and information for reseller companies of Safetech Innovations’ own products and products and services for which it acts as a distributor
Technology news
Articles written by Safetech Innovations describing how the solutions in the company’s portfolio work, the problems addressed, the benefits obtained, as well as aspects that require attention in order to achieve optimal results
Safetech Innovations S.A. has been providing cyber security services and solutions tailored to the needs of organizations since 2011. Many Romanian organizations have chosen Safetech's solutions and services for system integration, consulting, vulnerability management, operations outsourcing, security audit, in order to improve their level of cyber security.
On Feb. 6 2023 Safetech Innovations shares started trading on the Main Market of the Bucharest Stock Exchange under the symbol SAFE. This section contains information and documents intended for SAFE investors. For information on the evolution of share prices, we invite you to follow our profile on the BVB website.
Since 2011, we have maintained our strategic focus on cyber security, we act as a Managed Security Service Provider, and to date we have completed more than 600 testing and consulting projects and participated in more than 100 critical infrastructure security projects in the United States United, EU, China, India, Canada, Brazil, Morocco, Singapore, Philippines and New Zealand.
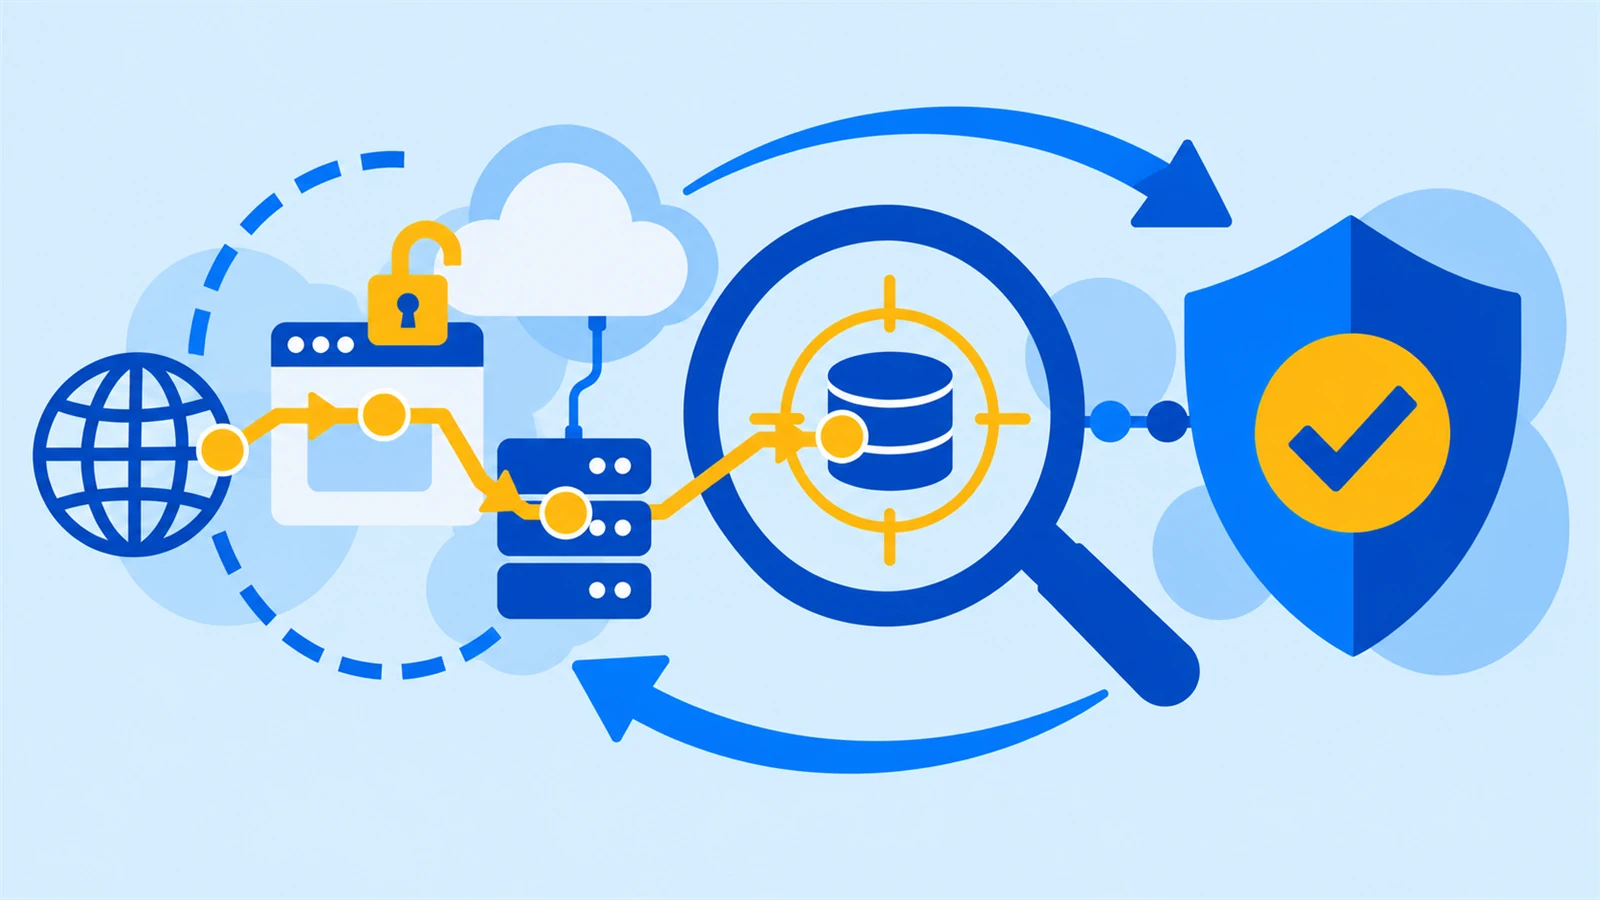
Security controls should also be evaluated by how they react to attack techniques relevant to the organization. The Safetech Innovations Breach and Attack Simulation Service — BAS — simulates controlled cyberattacks to verify the operation of protection, detection and response measures in the authorized perimeter.
The results show which techniques have been validated, what shortcomings have been identified and what measures can improve existing capabilities. The assessment is tailored to your infrastructure and objectives, with scenarios, limits and execution windows established prior to testing.
Utility and benefits
The BAS service is aimed at organizations that want to verify the effectiveness of controls already in place and understand where adjustments are needed. It can support teams operating a SOC or other detection and response capabilities, through technical results that can guide priorities for improvement. With the BAS service you get:
Validation of controls
Verification of the behavior of protection, detection and response measures for executed scenarios
Identification of deficiencies
Highlighting deficiencies that may affect the observation and treatment of tested attack techniques
A structured picture of coverage
Correlation of validated techniques with the MITRE ATT&CK matrix, within the limits of the evaluation
Priorities for improvement
Remediation and optimization recommendations that can be used by the responsible teams
Support for security decisions
Documented results for understanding the effectiveness of controls and planning for next steps
Service Characteristics
Breach and Attack Simulation services have the following characteristics:
Breach and Attack Tests Service
We simulate attacks under conditions agreed with the organization and analyze the results in relation to the project objectives. The focus falls on the practical validation of security capabilities: how controls behave in authorized scenarios and the detection and response deficiencies observed.
Validated techniques and MITRE ATT&CK
The techniques included are selected according to the objectives of the evaluation, the technical environment and the authorized limits. The MITRE ATT&CK matrix documents the techniques validated in the project and provides a common framework for discussing the results with the technical teams and management. The matrix shows the actual coverage of the simulations. The conclusions refer to the validated techniques, the analyzed perimeter and the conditions under which the verifications were carried out.
Tools and interpretation of results
The activities may use internal Safetech, Cymulate and PICUS tools, according to the scenarios and conditions of the project. The selection of tools follows the objectives of the assessment and the possibilities of the analysed environment.
The platforms support the execution and collection of results. Safetech specialists interpret the findings and formulate the recommendations in the context of the beneficiary’s infrastructure and processes.
Deliverables
At the end of the project, you receive:
BAS evaluation report — the results of the evaluation within the agreed scope and scenarios.
MITRE ATT&CK matrix with validated techniques — evidence of the techniques evaluated within the project.
List of identified detection and response deficiencies — findings that require the attention of the responsible teams.
Remediation plan and optimization recommendations — proposed measures to improve the analyzed capabilities.
The content and acceptance criteria of the deliverables are established at the initiation of the project. The implementation of the recommendations and any subsequent evaluations are defined separately, depending on the needs of the beneficiary.
Methodology and mode of collaboration
Methodology and project stages
Defining the objectives and the scope. We clarify which capabilities will be assessed, the systems included, the relevant scenarios and the results pursued. We establish the conditions of access, responsibilities and exclusions.
Preparation of simulations. We select the right techniques and tools and agree on the execution windows, the limits of the activities and the way to coordinate with the organization’s teams.
Controlled execution. We carry out authorized scenarios under the established conditions and collect the information necessary to evaluate the behavior of the controls.
Analysis of results. We correlate findings with tested techniques, identify detection and response deficiencies, and make recommendations for improvement.
Reporting and presentation of conclusions. We deliver the results and the remediation plan and explain the findings to the responsible teams, to support the establishment of the next measures.
The planning shall aim at the controlled conduct of the simulations in the authorised environment. The possible operational impact shall be analysed when defining the execution conditions and the activities shall be carried out within the agreed limits. The results shall document the behaviour of the controls for the scenarios assessed.
Availability and collaboration
The BAS service is available as a project.
The scope, scenarios, frequency, execution windows and testing limits are agreed for each engagement.
If you wish to re-check the controls after the changes, the objectives and conditions of a subsequent evaluation are set out separately.
BAS complements infrastructure penetration testing, which aims at the identification and authorized exploitation of vulnerabilities.
For monitoring and operational threat treatment, you can select SOC/MDR outsourcing services separately. These services have their own objectives and responsibilities and are contracted separately.
What recommends us?
The BAS service benefits from Safetech’s expertise in testing, solution integration, and security operations. This combination allows us to analyze simulation results in relation to the organization’s technical configurations, existing controls, and detection and response processes.
The evaluation is coordinated by specialists, who explain the results and the limits of coverage, so that your teams can identify relevant improvement measures. We correlate the findings with the assessed environment and the agreed objectives, turning the results of the instruments into applicable recommendations.