
Table of Contents
From Reported Vulnerabilities to Demonstrated Risks: What Can an Outside Attacker Exploit?
Is a vulnerability with a CVSS score of 9.8 always more dangerous than one with a score of 7.5? How relevant is a list of hundreds of critical vulnerabilities if we don’t know which of them can actually be exploited? And how can we demonstrate that remediation measures have eliminated the risk, not just the alert in a monitoring system?
These questions are becoming increasingly important for organizations operating complex IT infrastructures, distributed across their own data centers, cloud platforms, SaaS services, and systems managed by external vendors.
The ENISA Threat Landscape 2026 report, published in September, highlights that digital dependencies expand the attack surface and require a higher level of vigilance. Ransomware continues to be one of the most impactful threats, and the exploitation of known vulnerabilities remains an important vector for compromising systems.
The problem is not just the number of vulnerabilities. Scanning tools produce large volumes of findings, but they do not always reflect the real possibility of exploitation, the accessibility of the Internet system or the consequences on business processes.
For security teams, the challenge is to move from identifying potential vulnerabilities to demonstrating real risks and verifying their removal.
In this context, Safetech Innovations offers, through its partnership with KELA, access to ULTRA RED, a platform specialized in External Attack Surface Management (EASM) and Continuous Threat Exposure Management (CTEM).
The solution combines continuous discovery of exposed assets on the internet with active testing and validation of exploitability. Safetech specialists complement these capabilities through technical assessments, prioritization according to the customer’s operational context, remediation recommendations and retesting.
Importantly, ULTRA RED is an internationally awarded platform for innovation in cybersecurity, receiving the 2025 CyberSecurity Breakthrough Award and the 2024 Top InfoSec Innovator Award in the Continuous Threat Exposure Management (CTEM) category.
Identified vulnerability versus demonstrated exploitability
Most organizations already use vulnerability scanning tools. They identify vulnerable software versions, insecure configurations, or services associated with known CVEs and assign severity scores.
Although indispensable for vulnerability management, these tools have an important limitation: the identification of a vulnerability does not automatically demonstrate that it can be exploited in the particular configuration of the system.
For example, a scanner can report several critical vulnerabilities on a billing portal, starting from the web server version. However, the investigation may show that the vulnerable modules are not activated or that exploitation requires conditions that do not exist in that environment.
At the same time, a forgotten test subdomain can expose an administrative interface without authentication, connected to the production portal database.
This second issue may not have a CVE associated with it and, by implication, no CVSS score. However, exploiting it could allow access to customer data or compromise the billing process.
The difference between the two situations is essential:
- The reported vulnerability indicates the existence of a potential problem, based on the known software version, configuration, or signatures.
- The validated exposure demonstrates that the problem can be exploited under the tested conditions, through reproducible technical evidence.
- Business risk results from correlating this exploitability with the importance of the system, the accessible data and the operational consequences.
Therefore, prioritizing solely on the basis of CVSS can direct resources to issues that are not the most important avenues.
ULTRA RED: Continuous discovery and validation of the external attack surface
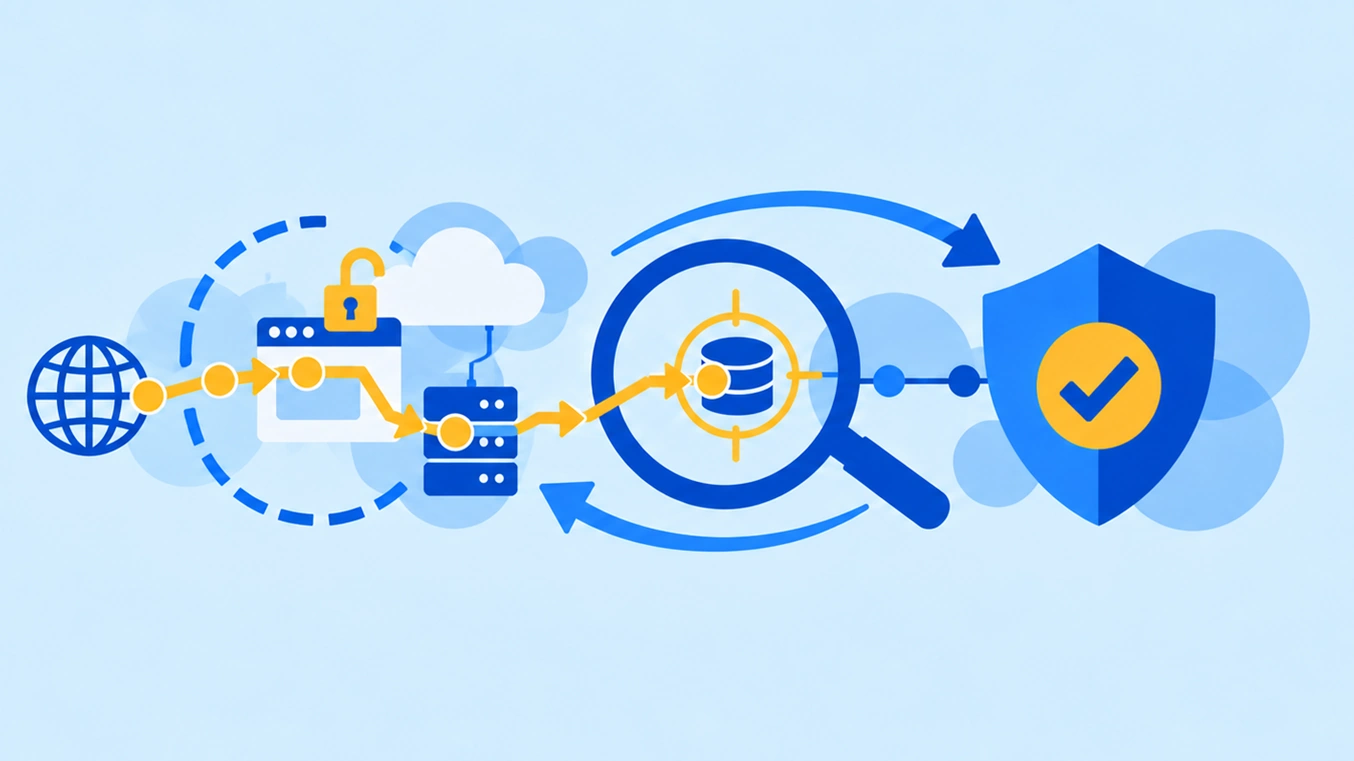
ULTRA RED assesses the organization’s infrastructure from the perspective of an outside-in attacker. The SaaS platform operates without agents and can start discovery from a single domain, recursively expanding the inventory of assets associated with the company. The process includes five main components:
1. External Attack Surface Discovery – identification of exposed assets
ULTRA RED identifies domains, subdomains, IP addresses, public services and cloud resources, including assets absent from the official inventory: test environments, shadow IT applications, legacy infrastructures or services operated by suppliers. Continuous monitoring detects new hosts, DNS changes, digital certificates, open ports and changes in exposed technologies. Safetech specialists verify the ownership of assets and correlate them with owners and business processes.
2. Active Testing – verifying operability
The platform performs active, controlled and non-intrusive tests to confirm the exploitability of known vulnerabilities, misconfigurations or exposed administrative interfaces. Unlike scanning based on software versions and CVEs, deterministic validation aims to demonstrate a real path of exploitation, within the limits of the authorized area and without affecting production systems.
3. Exposure Validation – reproducible technical evidence
For confirmed exposures, ULTRA RED provides the affected asset, operating conditions, Proof of Concept (PoC) proofs, relevant HTTP requests and responses, and the technical context required for remediation. Validation is specific to the asset, timing, and conditions tested; the absence of a finding does not guarantee the security of the system. Authentication-enabled applications, complex chains of operation, and internal scenarios may require manual penetration testing performed by Safetech.
4. Contextual Risk Prioritization
ULTRA RED correlates exploitability with technical severity and criticality of assets. For CVE vulnerabilities, indicators such as CVSS and EPSS (Exploit Prediction Scoring System) are used, complemented by Safetech with CISA KEV information about the vulnerabilities actually exploited. Threat intelligence data from the KELA ecosystem adds context about the technologies targeted by attackers and the activity of ransomware groups. Safetech integrates the importance of applications, data processed, operational dependencies and compensatory controls, so that priorities reflect exploitability, probability of attack and impact on the business, not just the CVSS score.
5. Remediation Verification – confirmation of the fix
After the implementation of corrective measures, ULTRA RED automatically retests the findings that allow this verification, to confirm the elimination of the exploitation vector. Complex problems are manually rechecked by Safetech specialists. Each finding is tracked until the confirmed closure, with evidence and audit history. Continuous monitoring identifies possible re-occurrences of exposures or changes that introduce new risks.
The result: a continuous process of discovery, validation, prioritization and verified remediation, which turns vulnerability lists into demonstrated risks and concrete security actions.
ULTRA RED and Continuous Threat Exposure Management
The ULTRA RED approach is part of the concept of Continuous Threat Exposure Management (CTEM), which aims to identify and continuously reduce exposures relevant to the organization.
A CTEM program involves delineating the analyzed area, discovering assets, prioritizing risks, validating exploitability and mobilizing the teams responsible for remediation. ULTRA RED automates important components of this process, especially the discovery, testing and validation of external exposures. For the effective implementation of CTEM, however, technology must be integrated into the organization’s operational processes.
This is where Safetech Innovations comes in, by establishing the evaluation area, interpreting the findings, defining responsibilities and coordinating remediation and retesting activities.
Such an approach allows the organization to track not only how many vulnerabilities have been identified, but also how quickly new exposures are discovered, how many of them are exploitable, and to what extent validated risks are eliminated.
Complementary services offered by Safetech Innovations
ULTRA RED ensures the continuous discovery and validation of external exposures, and Safetech Innovations complements the technology with specialized testing, monitoring, remediation and risk management services. Depending on the infrastructure and requirements of the organization, these include:
• Manual penetration testing and advanced security assessments
The Safetech team conducts penetration tests for web applications, APIs, systems that require authentication and complex exploitation scenarios, including using OWASP methodologies. The assessments cover authentication, authorization and access control mechanisms, as well as attack chains that cannot be automatically validated.
• Monitoring and response to incidents through STI CERT
Through STI CERT, Safetech provides 24/7 security monitoring, event analysis and incident response. ULTRA RED findings can be correlated with SIEM data to identify exploitation attempts, and authorized tests can be coordinated with the SOC team to verify the effectiveness of detection mechanisms.
• Security assessments for OT and industrial infrastructures
ULTRA RED identifies external access points, such as VPNs and remote management portals. To assess OT networks, Safetech uses specialized methods and technologies, including ICS Detect and Radiflow solutions, tailored to the availability and safety requirements of industrial infrastructures.
• Technical consulting and remediation support
Safetech specialists turn validated findings into recommendations tailored to the customer’s infrastructure: software updates, changes in access policies, segmentation, disabling vulnerable services or implementing compensatory controls. When a definitive fix is not immediately possible, temporary measures such as WAF/IPS rules and access restriction can be applied.
• Operational integration, governance and reporting
ULTRA RED results can be integrated with SIEM platforms, ticketing systems, and vulnerability management processes, via portal, API, and data exports. Safetech tracks findings, responsibilities, deadlines, and evidence of retesting, providing notifications for critical exposures, monthly executive reports, and quarterly summaries for CISOs and boards. This information also supports the documentation of risk management measures in the context of NIS2 and DORA.
What tangible benefits do you gain with ULTRA RED and Safetech Innovations?
Fewer irrelevant alerts, evidence-based remediation priorities, and a clear picture of real risks.
For example, ULTRA RED can identify a forgotten subdomain, on which an administrative interface accessible without authentication operates. The platform technically validates the exposure and provides evidence of exploitability. Safetech analyzes the impact on the company’s systems and data, sets the priority and recommends the necessary measures. After their implementation, the retest confirms the elimination of the identified attack vector.
The process doesn’t stop there. Continuous monitoring allows for the detection of new assets and re-emergent exposures. For security teams, this approach means less time spent on unconfirmed alerts and more efficiency in remediating exploitable risks.
For CISOs and management, the results are measurable: validated exposures, impacted critical assets, remediation timelines, retest confirmed closure rate, and risk evolution over time. This information supports investment decisions, security governance, and documentation of necessary measures in the context of NIS2 and DORA.
How can you find out what an attacker from outside your organization can exploit? Simple. Ask the Safetech Innovations team for an initial assessment of the external attack surface with ULTRA RED. You will receive, for the agreed area, an image of the exposed assets, evidence for the exploitable vulnerabilities identified, and a remediation plan prioritized according to the risk to the business.
Contact Safetech Innovations to schedule an assessment at [email protected].